

How Does Obsolix Work?
The Edge decides on site, the Central analyzes at the core, and a one-way encrypted connection links them. Every component runs within your organization's boundary.
Edge + Central Architecture
Clients query the on-site Edge; the Edge decides within milliseconds and forwards logs to the Central.
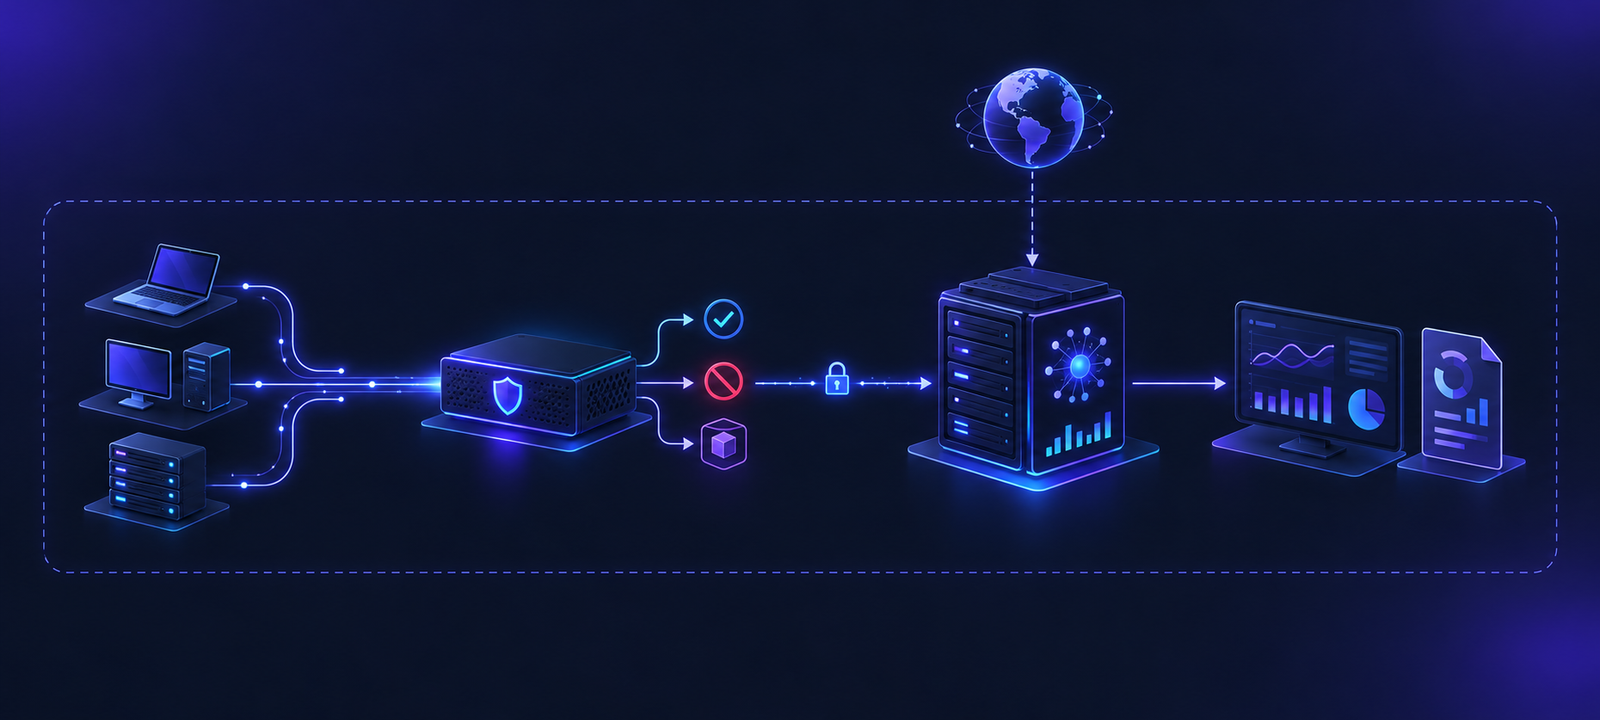
Four Components, One Chain
Every step, from where the query is received to the report, is completed in-house.
- 01
Edge
Runs in front of the organization's DNS server at each site and forwards, blocks or quarantines each query within milliseconds based on threat intelligence, the behavior engine and policy rules. It keeps deciding even if the internet connection drops.
- 02
Central
Logs from every Edge are collected in one place; the AI model scores behavior, user and organization risk analyses are produced, reports are prepared and data is forwarded to the SIEM.
- 03
Secure Connection
The Edge connects to the Central over a one-way encrypted connection; the Central never opens a connection toward the Edge. Policy changes are distributed as signed packages. During an outage, logs wait locally and are delivered without loss.
- 04
Deployment
On Kubernetes, with ready-made profiles from small to large. After deployment, protection continues uninterrupted in environments without internet access; updates are installed as packages, and your existing DNS servers stay the same.
The Journey of a Query
Five steps completed within milliseconds.
- 1
The query reaches the Edge; policy rules and threat intelligence are checked.
- 2
The behavior engine evaluates the query: DGA, tunneling, NXDOMAIN, fast-flux, brand impersonation.
- 3
A verdict is made: forward, block or quarantine.
- 4
The log is sent to the Central over the encrypted connection; during an outage it waits locally.
- 5
The Central scores it with AI, feeds it into user and organization risk analysis, and forwards it to the SIEM and reports.
Let's tailor the architecture to you
A single site or hundreds of branches: let's plan your Edge + Central layout together.