

Where Does the Data Stay?
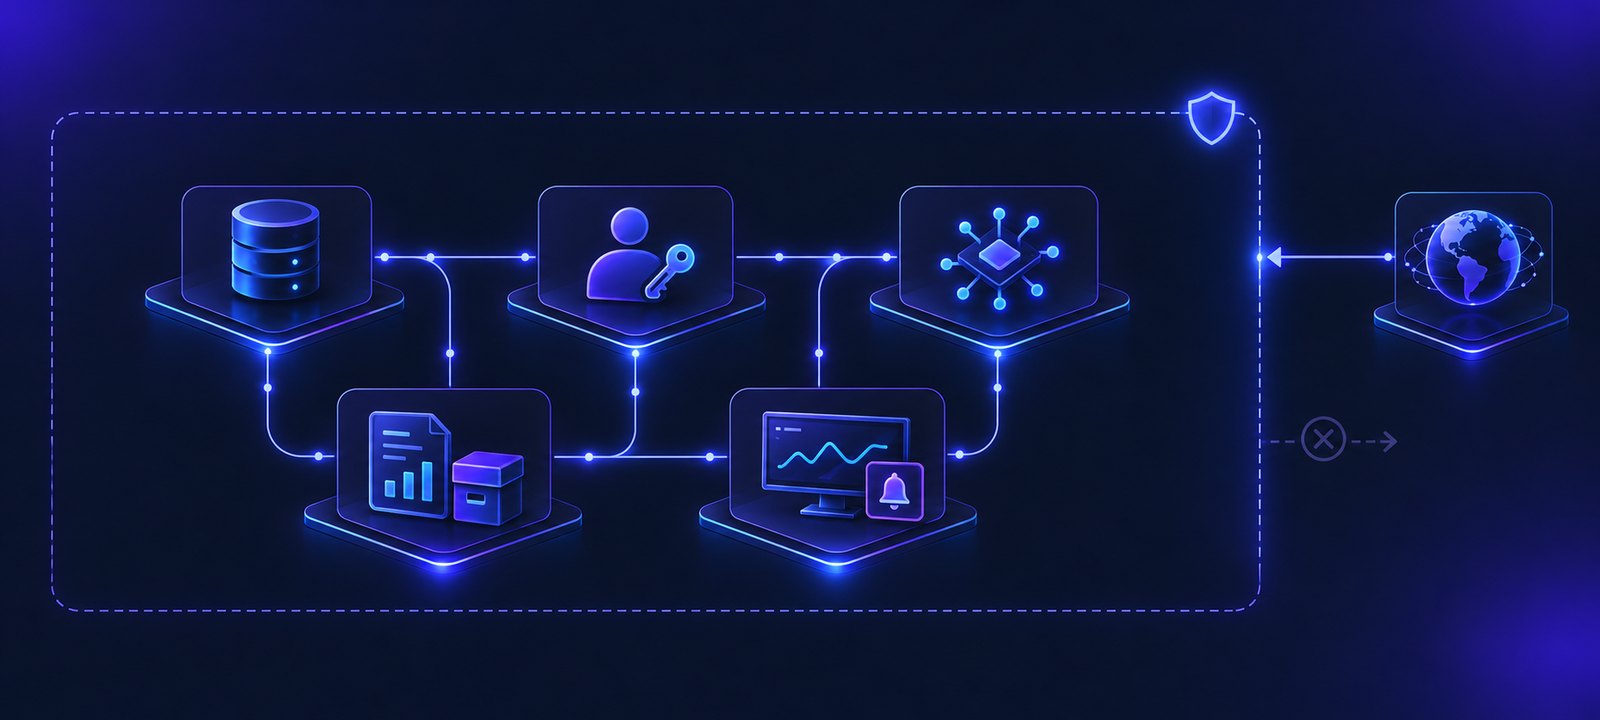
In Obsolix, DNS logs, source addresses, user mappings, AI analyses and reports are kept only on your organization's servers. The system sends no data out; it only downloads threat intelligence updates.
Inside the Organization Boundary
Everything stays inside; only threat intelligence updates come in.
Regulation and Product Security
Position on public-sector information security, KVKK, domestic software and product security.
Public-Sector Information Security
Aligned with the principle of Turkish Presidential Circular No. 2019/12 that "data belonging to public institutions shall not be stored in cloud services located abroad": Obsolix runs on the institution's own systems.
KVKK
DNS logs are personal data under KVKK, Türkiye's Personal Data Protection Law. Since Obsolix involves no cross-border transfer, the transfer obligations under Article 9 of KVKK do not arise.
Domestic Software
R&D and engineering are done in Ankara. It qualifies for the price advantage granted to domestic software in Turkish public tenders.
Product Security
Encrypted Edge–Central connection, signed policy and update packages, role-based access, signed container images.
Let's answer your compliance questions
Our team will get back to you on technical and legal questions about KVKK, public-sector information security and procurement.